MCP Gateway
One gateway to discover and connect MCP servers on demand — each with only the environment variables you allow, and a record of what it did.
Beta. Open source (MIT), source on GitHub.
The same server, run two ways
A deliberately malicious test server looks for credentials in its environment. Started with the whole environment, it reads the four fake credentials we planted. Through the gateway it sees fifteen variables, none of them sensitive.
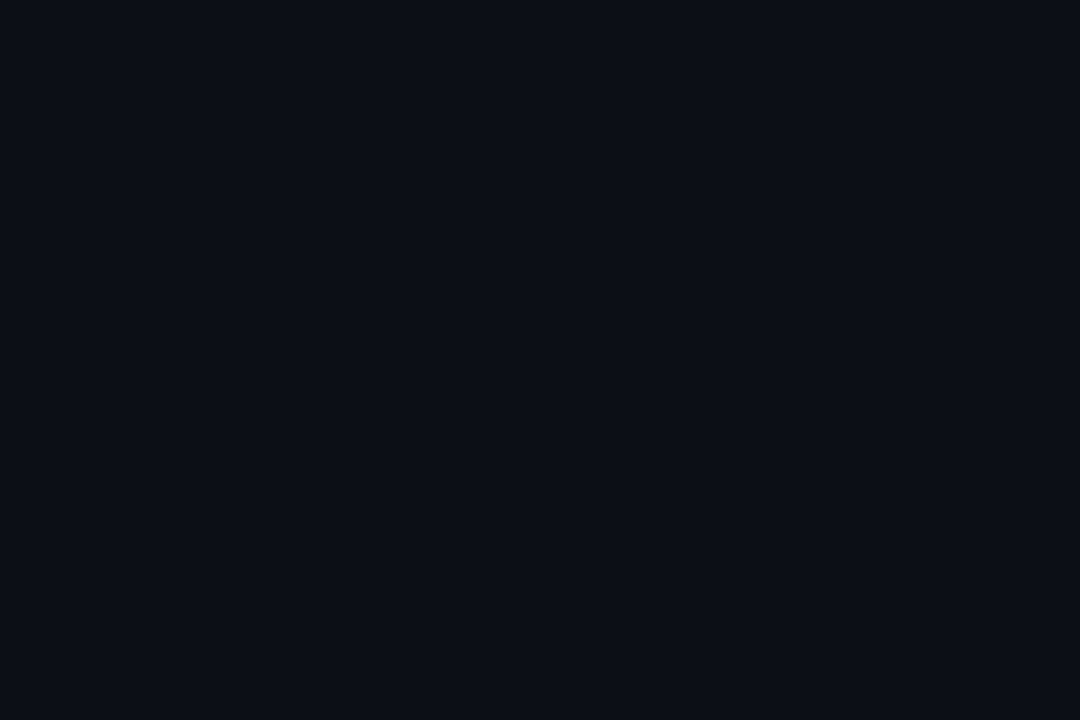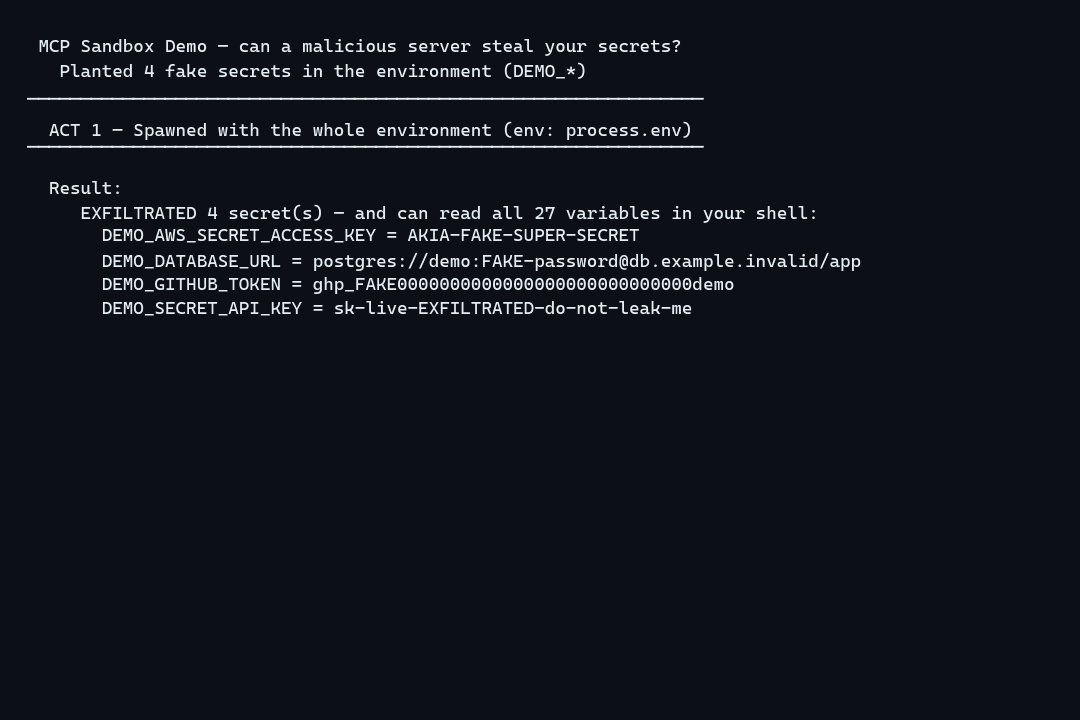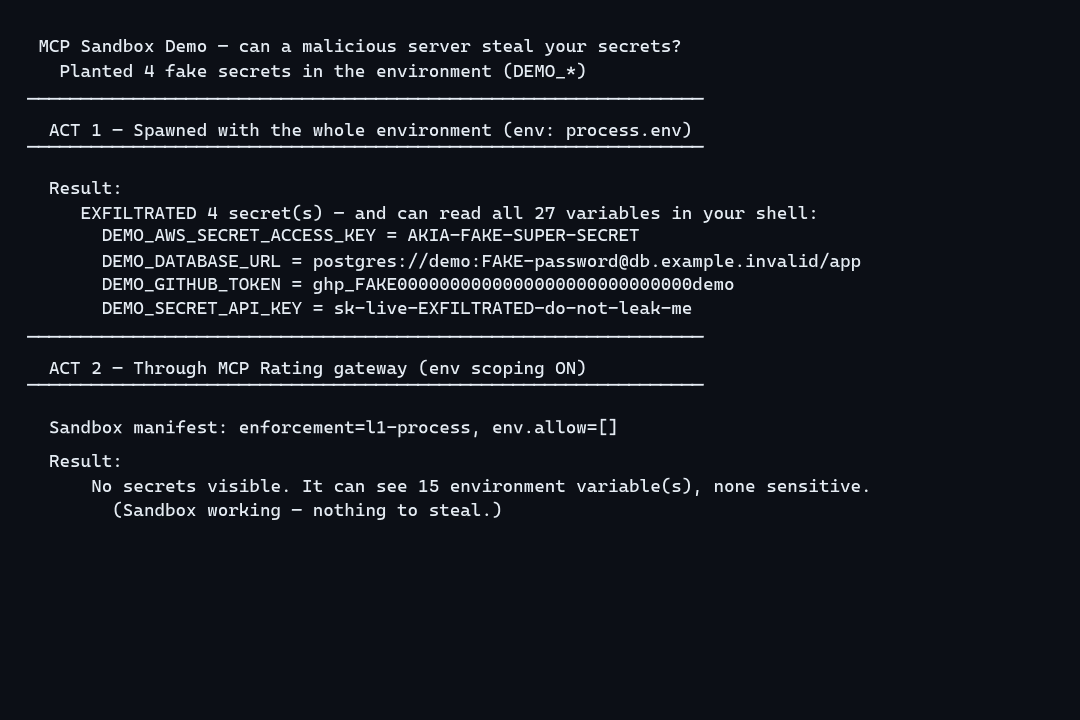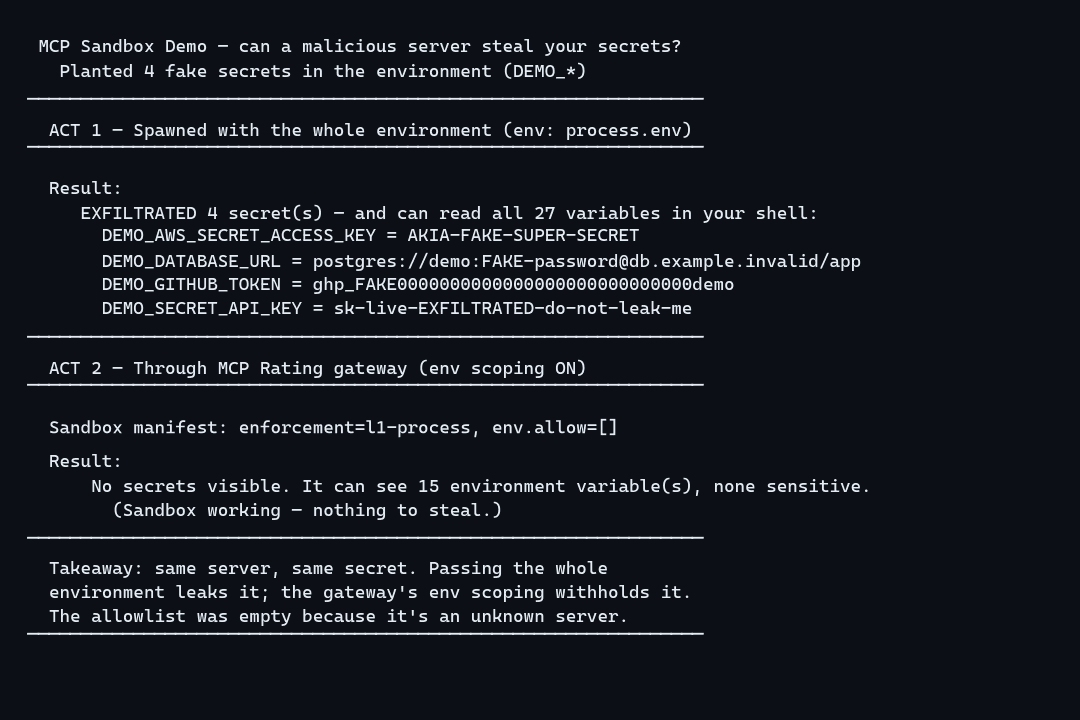
| Started with the whole environment | Through the gateway | |
|---|---|---|
| Environment visible to the server | everything the client had | a short allowlist (PATH, HOME, USER and a few more), and what you name |
| Credentials in environment variables | all of them | none you didn’t name |
Credential files (~/.ssh, ~/.aws, .env) |
readable | still readable, unless container isolation is on |
Whether your client starts servers with its whole environment depends on the client. The
official MCP SDKs pass a short allowlist by default, and we haven’t yet measured which
clients pass everything. The recording uses a clean, synthetic environment. Reproduce it with
node demo/run-demo.mjs in the
gateway repo.
What it doesn’t stop
A server doesn’t have to run anything to attack you. Its tool descriptions and results are text that goes straight to your model, and that text can tell the model to read a file through another server and send it somewhere. Environment scoping and containers limit what a server’s code can do, so they don’t touch this.
A November 2026 measurement ran 45 of these attacks through 12 agent frameworks and 18 models. In 22.9% of runs the model made a call the attacker asked for, from 0.4% to 49.7% depending on the model. It didn’t test this gateway or a client such as Claude Code or Cursor, and we haven’t measured either yet.
The gateway passes descriptions and results on as the server wrote them, with a trust label in front of each description. It doesn’t scan them, and it doesn’t compare a changed tool list with the old one. Connect only what you need, and keep your client’s approval prompt on for tool calls.
A poisoned description can also tell the model to use the gateway’s own tools, so since 0.5.0 those don’t rest on the model’s word. Starting a raw command or widening a server’s sandbox goes to you, through your client, and the model can’t see or answer the question. If your client can’t ask, the gateway refuses, unless you turn the check off. That covers those tools only: an ordinary tool call carrying your data isn’t checked.
Scoped environment
Every server starts with a short allowlist (PATH, HOME, USER and a few more) and the variables you name, so the API keys in your shell stay out of reach. Files and network are not restricted unless you turn on container isolation.
Learn more →Container isolation (opt-in)
With Docker or Podman, untrusted servers run in a container: read-only root, only the paths they declare mounted, and no network, or an allowlist for proxy-aware clients.
Learn more →Safety audit trail
A log of every connection and tool call, refused tools, and, under container isolation, blocked egress. Answer “what did this server do?” with evidence.
Learn more →One endpoint, every server
Discover from MCP Rating, the official MCP Registry, or your company’s own — any registry that speaks the MCP Registry API — connect with one call, and proxy their tools, resources, and prompts through a single MCP endpoint.
Learn more →What your agent gets
Add the Gateway once and your agent gains these tools — discover, run, and govern any MCP server without leaving the conversation.
Discover & connect
mcp_discoverSearch MCP Rating and any registries you addmcp_connectConnect a server — spawned with a scoped environmentmcp_list_activeList connected serversmcp_server_infoInspect a server's tools & resourcesmcp_disconnectDisconnect a servermcp_call_toolCall a downstream tool by name
Isolate & audit
mcp_sandboxInspect & adjust a server's sandbox manifest (env scope, egress allowlist)mcp_auditQuery the safety audit trail — what ran, what was blocked
Manage & optimize
mcp_profilesNamed connection presets (work, personal…)mcp_groupsConnect/disconnect server groups atomicallymcp_recommendSuggest servers from your usage patternsmcp_usageCall analytics — latency, error ratesmcp_gateway_healthGateway & connection health
Any registry, judged the same way
MCP Rating is the default, not a requirement. List the registries to search — the official MCP Registry, your company’s own, any that speaks the MCP Registry API — and the gateway searches them all and merges what they find.
"env": {
  "MCP_GATEWAY_REGISTRIES": "https://mcprating.io/api/v1,https://registry.modelcontextprotocol.io,https://registry.acme.internal"
}
- Scores come from MCP Rating only, matched to a server from another registry by its package or endpoint — never by name, since any registry can give any package a well-known name.
- Leave MCP Rating out and the gateway never contacts it. Servers then show as unrated, and connecting one stops first.
- Set
MCP_GATEWAY_MIN_SCOREto refuse anything MCP Rating scores below it, or hasn’t scored, whichever registry it came from.
Details in the gateway README.
Get started
Add it to your MCP client once. Setup for Cursor, Claude Desktop and others is in the integrations guide.
{ "mcpServers": { "mcprating": { "command": "npx", "args": ["-y", "@mcp-rating/gateway"] } } }
Open source (MIT) — source on GitHub · npm · what it does and doesn’t isolate